AWS SSO: the setup I should have done years ago
How we replaced root logins and long-lived access keys with AWS SSO, one account per client, and guardrails that apply to everyone.
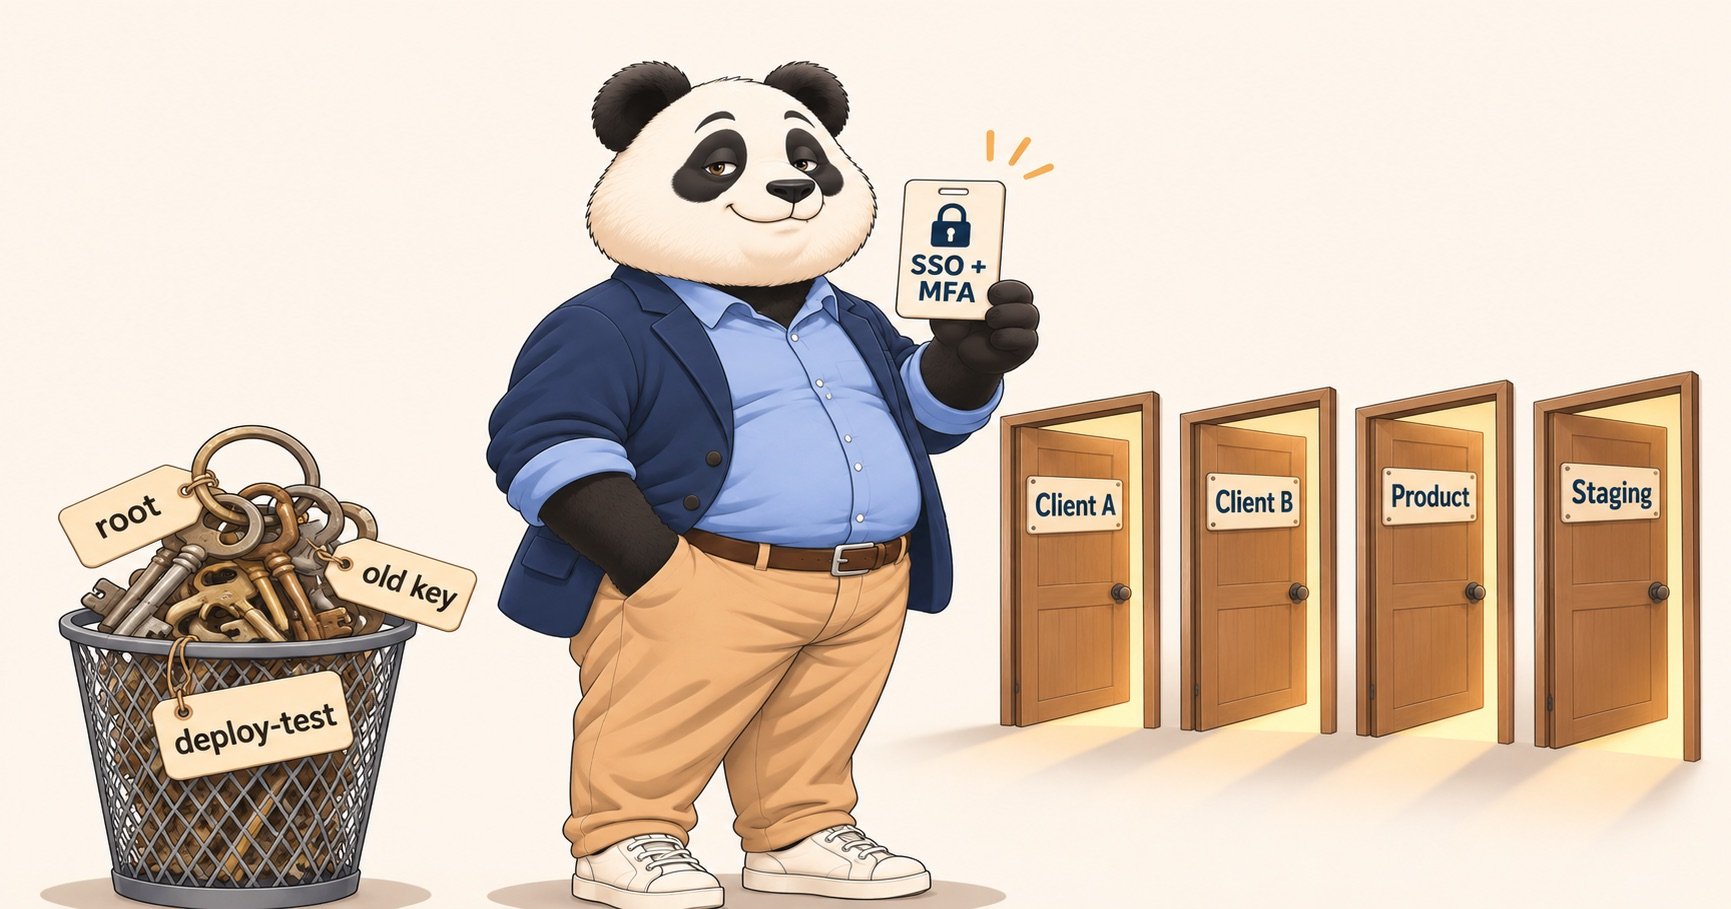
Until recently, every AWS account we had came with its own root login. Deployment tests used access keys, some of them in config files (kept out of git, and all rotated since). It worked, but each one was a password or a key that never expired. AWS tells us to rotate keys. Honestly, how many of us do? I didn't.
Now only the management account has a root login. Everyone signs in through SSO with MFA. Code and scripts use named profiles, so a test only runs while my SSO session is active. No person on the team holds a long-lived key any more.
With AI tools making attacks cheaper and faster, I wanted our infrastructure locked down properly. Moving our servers to AWS was the push to do it. This post explains the setup, step by step, for a small team with several clients. Almost nothing here costs extra: IAM Identity Center, Organizations and service control policies are free.
Three ways into AWS
Root user | IAM users | SSO (IAM Identity Center) | |
|---|---|---|---|
What it is | The email and password that created the account | A user and password or access keys, inside one account | One login for every account in the organisation |
Can be limited | Not within its own account | Yes | Yes, per account and per role |
Keys on laptops | Possible | Usually, and they never expire | No, sessions expire after hours |
Many accounts | One login per account | One user per account | One login, pick the account |
Someone leaves | Change the password everywhere | A nightmare: which user, which key, which application? | Disable one user |
The IAM users column is the one that hurts. AWS tells you when a key was last used, but not directly which application or laptop it lives in. Without good documentation, deleting a key means guessing what will break.
Root should almost never be used. IAM users made sense when you had one account. Once you have more than one, SSO is the better default.
Step 1: one AWS account per client or product
AWS Organizations lets one management account own many member accounts. We use a separate account for each client or product, and for each environment, plus one for internal tools.
Why bother:
- Blast radius. A mistake or a leaked key in one account stays contained in that account.
- Billing. Each client's cost is its own line, no tagging needed.
- Handover. If a project ever changes hands, the whole account can move to another organisation. That's far easier than migrating the setup piece by piece.
The management account runs nothing. It only holds billing, SSO and the policies.
Step 2: people sign in with SSO
IAM Identity Center has three ideas:
- Users and groups. The people, each with MFA.
- Permission sets. What a role can do.
- Assignments. Which group gets which permission set in which account.
Everyone signs in at one portal and sees only the accounts they're assigned to.
We use three permission sets:
Permission set | For |
|---|---|
| The owner |
| Building and deploying |
| Looking, including for AI tools |
Developers get the Developers set only in the accounts they work on. Everywhere else they get view-only or nothing.
Sessions are short on purpose. A portal sign-in lasts 4 hours, then it's password and MFA again. Each account session lasts 2 hours, whatever the role. AWS's defaults are 8 hours and 1 hour. For comparison, NIST's guidance recommends signing in again at least every 24 hours, and requires it every 12 hours at its strictest level.
Step 3: the CLI, without access keys
This is the part that sold me. In ~/.aws/config (AWS guide):
[sso-session company]
sso_start_url = https://<your-id>.awsapps.com/start
sso_region = us-east-1
sso_registration_scopes = sso:account:access

[profile client-a]
sso_session = company
sso_account_id = 111111111111
sso_role_name = Developers
region = eu-west-1

[profile client-b]
sso_session = company
sso_account_id = 222222222222
sso_role_name = ViewOnlyAccess
region = eu-west-1
Then:
aws sso login --sso-session company     # opens the browser once
aws s3 ls --profile client-a            # any profile in the session now works
One browser login covers every account. The credentials are temporary: the CLI renews them on its own while the portal sign-in is active, and after 4 hours it's aws sso login again. There's nothing long-lived on disk to leak.
Step 4: remove root from member accounts
AWS now lets you delete the root credentials of member accounts centrally (IAM → Root access management). We did that for every member account. Only the management account keeps a root login, with two MFA devices.
If root is ever needed on a member account, the management account can allow a password recovery for it, as a deliberate one-off. With this turned on, accounts created inside Organizations start without root credentials; accounts you invite need them removed.
Step 5: guardrails for member accounts
Region lock. A service control policy denies requests to any region other than the two we use. Global services (IAM, CloudFront, Route 53, WAF and so on) are exempt. A leaked session can't start servers in a region nobody watches. One statement, trimmed:
{
  "Sid": "DenyOutsideAllowedRegions",
  "Effect": "Deny",
  "NotAction": ["iam:*", "sts:*", "cloudfront:*", "route53:*", "wafv2:*", "..."],
  "Resource": "*",
  "Condition": {
    "StringNotEquals": { "aws:RequestedRegion": ["eu-west-1", "us-east-1"] }
  }
}
No deleting by hand. The Developers permission set adds a deny for destructive actions: terminating instances; deleting databases, backups and log groups; stopping CloudTrail. The trick is the aws:CalledVia condition: the deny doesn't apply when CloudFormation makes the call. So deletes have to go through CloudFormation, where our infrastructure-as-code deploys show them in a diff first, not as a direct console click or CLI call. It's a guard against accidents, not against a determined attacker. Again one statement, trimmed:
{
  "Sid": "DenyIrreversibleDeletes",
  "Effect": "Deny",
  "Action": ["ec2:TerminateInstances", "rds:Delete*", "backup:Delete*",
             "logs:DeleteLogGroup", "cloudtrail:StopLogging", "..."],
  "Resource": "*",
  "Condition": {
    "ForAllValues:StringNotEquals": { "aws:CalledVia": ["cloudformation.amazonaws.com"] }
  }
}
The same permission set also can't read secret values.
This isn't the strictest setup possible. Only a small, trusted team has access, so I left some room for them to work without asking me for every change. You can lock it down much further. Treat it as a starting point, not a template.
Audit. One organisation-wide CloudTrail logs every management API call in every account and enabled region, new accounts included, and keeps it for a year.
Step 6: a checklist for every new account
- Create it in Organizations, with a naming convention for the account email.
- Attach the region policy.
- Check root access management shows no root credentials.
- Assign SSO access.
- Update the docs.
Those docs, and the JSON for every policy, live in a git repo. For now, a change is made in the console, the JSON is updated to match, and it's committed. The whole setup is written down, and the history shows every change.
How we rolled it out without breaking anything
The risk with a change like this isn't the new setup. It's what quietly depends on the old one.
So the first step was read-only access for Claude. With it, Claude went through every account: users, roles, which access keys existed and when they were last used, policies, and what depended on them. From that we planned the change one step at a time.
The rule was simple: running applications don't change. Only two things did: how people sign in, and how future deployments get their credentials. Each step was small enough to check before the next one, and nothing deployed went down.
A few older applications still use access keys. Those keys stayed, but each one now allows only the actions that application needs, and only from its own server. A leaked key is far less useful anywhere else.
Where to start
If you do only one thing this week: turn on IAM Identity Center, move yourself to an SSO profile, and deactivate your own access keys. Delete them once you're sure nothing breaks. The rest can follow one step at a time.
Was it worth it?
The switch took an afternoon. Knowing what depended on the old setup was the real work. Now nobody on the team holds a long-lived AWS key, adding a client is a checklist, and removing a person is one click, with their sessions running out within two hours. I should have done it years ago.
- Category
Discussion
No comments yet